This Week in Crypto Law (November 15, 2026)
Law and Ledger is a news segment focusing on crypto legal news, brought to you by Kelman Law – A law firm…
The November 12 investigation reports 25 operations against at least 19 organizations during August–September, with humans assigning targets and able to steer. Read the full story on CryptoSlateUnderstand the crypto…
Make CryptoSlate preferred on
Share Share
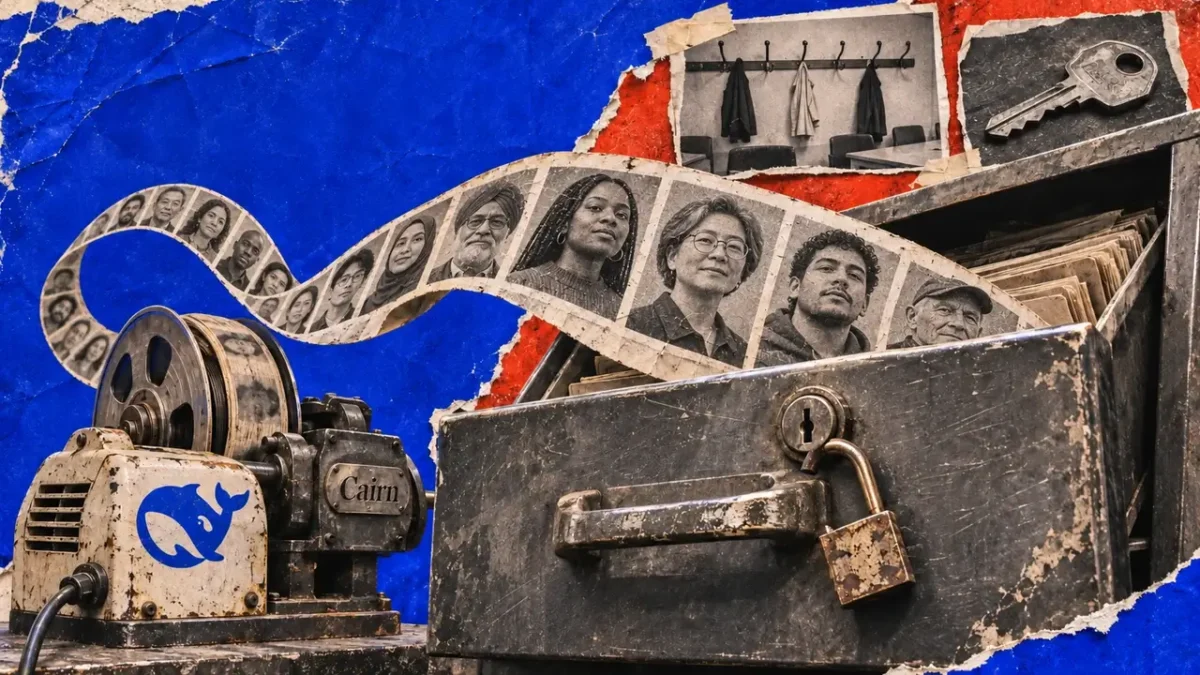
AI-assisted attacks accessed systems or retrieved data at 10 organizations, according to a November 12 investigation by Palo Alto Networks’ Unit 42. The security research team tracked 25 operations against at least 19 organizations during August and September 2026, including semiconductor companies, defense and policy organizations, and civil-society groups.
Unit 42 said the attackers used a customized version of Cairn, an open-source framework for AI-driven penetration testing, paired with Zhipu GLM and DeepSeek models.
The reported outcomes went beyond reconnaissance. The researchers reported unauthorized access to a semiconductor company’s production system and to more than one million member records at a US teachers’ union.
Attackers also modified a live standards-ballot document and obtained nonpublic data at an industry standards organization, the researchers said.
Humans supplied targets and goals, sometimes adding intelligence gathered beforehand. The framework then planned, executed and recorded subsequent work.
Individual operations lasted from 20 minutes to more than 50 hours, Unit 42 reported, with human steering still possible.
Activity: August–September 2026. Report: November 12, 2026. Unit 42 describes human-directed AI intrusions with continued steering possible.
Humans chose targets and could keep steering while agents repeated the intrusion work.
Campaign outcomes are Unit 42’s findings. The diagram shows the design, not measured human-intervention frequency. Operations and organizations are different units; no success rate is inferred.
Sources and evidence
Conceptual workflow from Unit 42’s description and Cairn’s documentation. Arrows show task and information flow, not measured timing. Counts reproduce the report and use distinct units; no ratio or general success rate is calculated.
Campaign outcomes are Unit 42’s findings. The diagram shows the design, not measured human-intervention frequency. Operations and organizations are different units; no success rate is inferred.
Infographic by CryptoSlate
That arrangement let humans direct the campaign while agents sustained the intrusion work. Unit 42 assessed that a single operator or small team likely ran the activity and argued that autonomous orchestration expanded the number of simultaneous attempts they could sustain.
Unit 42 concluded that AI increased the scale and reach of the campaign, not its technical sophistication.
The November 12 investigation adds quantified outcomes to earlier reporting on AI-assisted attacks. CryptoSlate’s November 5 coverage of CERT-In’s CRAFTY FALCON advisory already named Cairn among AI-assisted offensive-security tools. The reports describe different observed activity; shared tooling does not establish a link between their operators.
Unit 42 assessed with moderate confidence that the activity it tracked represented China-nexus intelligence collection, based on language, tooling and target selection.
For defenders, the report’s practical warning is that familiar gaps can support prolonged, coordinated intrusion attempts. Unit 42 says identity hygiene, reducing exposed attack surfaces and software patching remain effective.
Liam ‘Akiba’ Wright Editor-in-Chief • CryptoSlate
Also known as “Akiba,” Liam Wright is a reporter, podcast producer, and Editor-in-Chief at CryptoSlate. He believes that decentralized technology has the potential to make…
AI
2 min read 17 hours ago
Nov 14, 2026 Bearish
Law and Ledger is a news segment focusing on crypto legal news, brought to you by Kelman Law – A law firm…
Brazil's central bank stance on stablecoin conversions could reshape fintech operations, emphasizing stricter compliance and potential market shifts. The post Brazil’s central…
Law and Ledger is a news segment focusing on crypto legal news, brought to you by Kelman Law – A law firm…
Angry Token price today, ANGRYTOKEN to USD live price, marketcap and chart CoinDesk