S&P Global Targets $10B Blockchain Lending Market With New Risk Tool
S&P’s Vault Risk Assessment weighs six risks in DeFi lending as vault deposits reach $10 billion, but it is not a credit…
Consensys found no compromised assets or data, no malicious code deployment and no user impact, but contractor access controls face scrutiny. The post MetaMask code was open to a North…
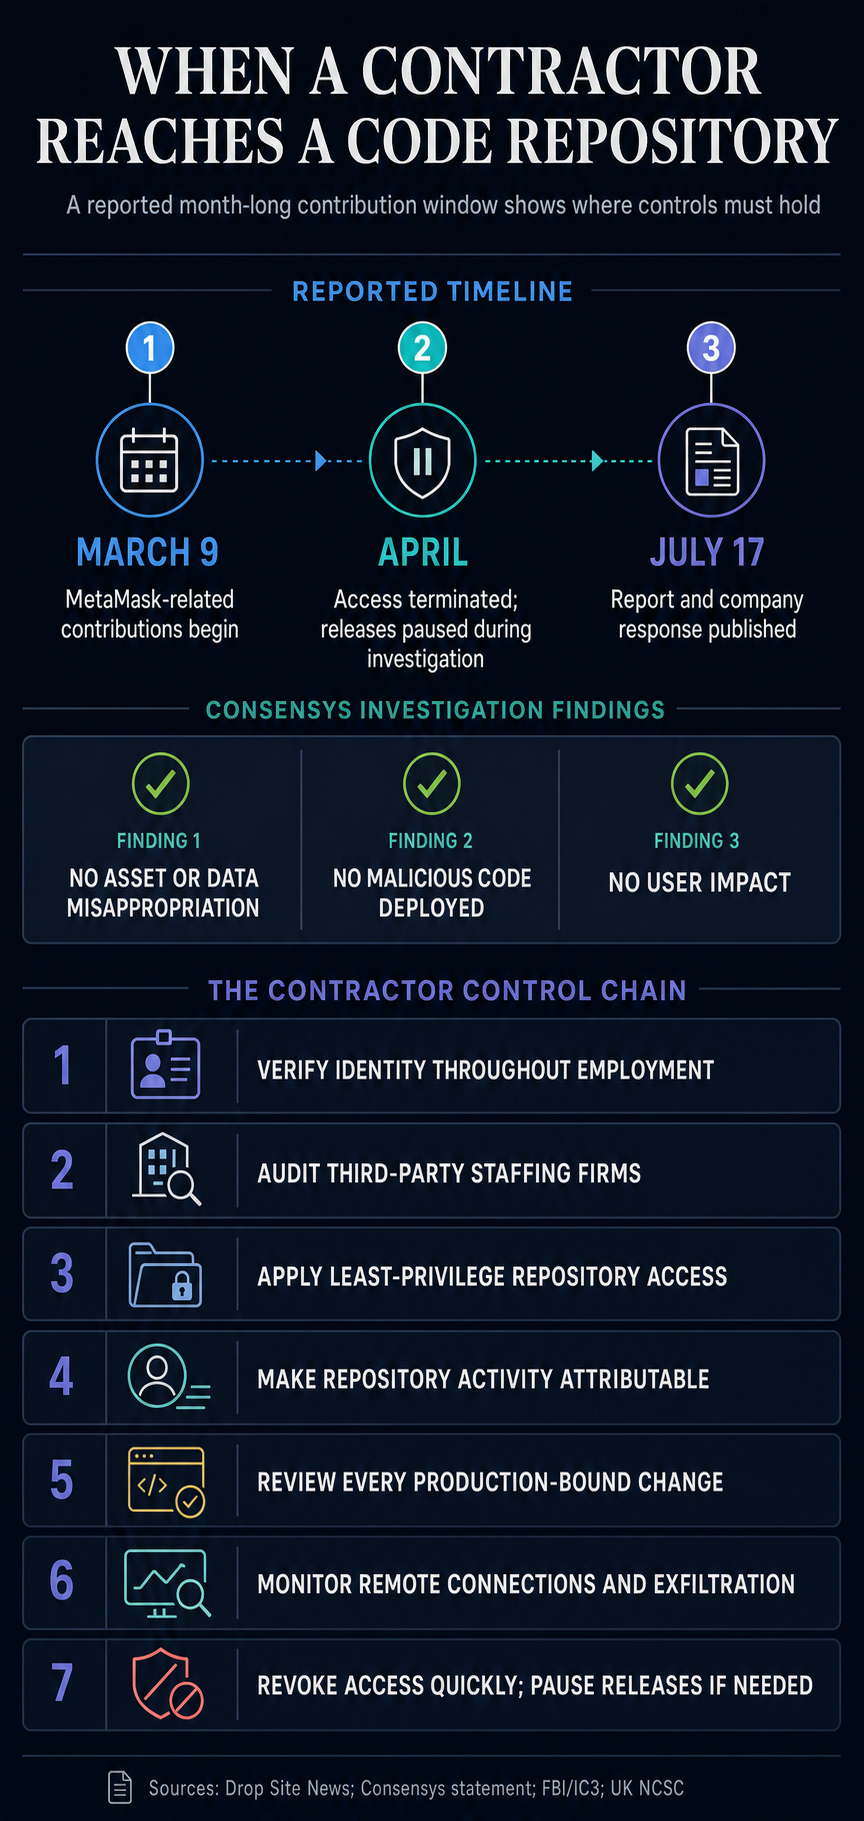
A contractor brought in through a third-party provider worked on MetaMask code from March 9 until Consensys cut off access in April. Consensys later described the person as linked to North Korea.
Consensys said its investigation found no misappropriation of assets or data, no malicious code deployment and no impact to user safety or security. General counsel Matt Corva said the company identified the threat quickly, terminated access, launched a comprehensive investigation and notified law enforcement.
Drop Site reported that an internal April alert ordered all product releases suspended pending the investigation and told staff not to interact with the consultant. Corva called the service provider relationship reputable and said Consensys has since reviewed its third-party service practices, so the rigorous standards applied to employees also cover more complex outside relationships.
Related Reading
The bigger risk after Drift may be the access attackers gain before a protocol knows it has a problem.
Apr 8, 2026
·
Gino Matos
The incident gives no indication that user accounts or wallet assets were compromised. Consensys’ existing relationship with the vendor still left a gap: every contractor and account needed its own safeguards.
MetaMask’s general security guidance warns that malicious workers can use false identities and forged documents to obtain remote roles. It recommends checks using actual documents, multiple interviews, hardware authentication, IP and location verification, reference checks, and limits on access to critical systems.

Related Reading
Researchers watched in real-time as the Famous Chollima division used this common remote work setup to bypass firewalls.
Dec 3, 2025
·
Oluwapelumi Adejumo
The FBI has separately warned that North Korean IT workers have used company-network access to copy code repositories. Its guidance calls for identity verification during interviews, onboarding and throughout employment, routine audits of third-party staffing firms, least-privilege access and monitoring for unusual remote connections or repository exfiltration.
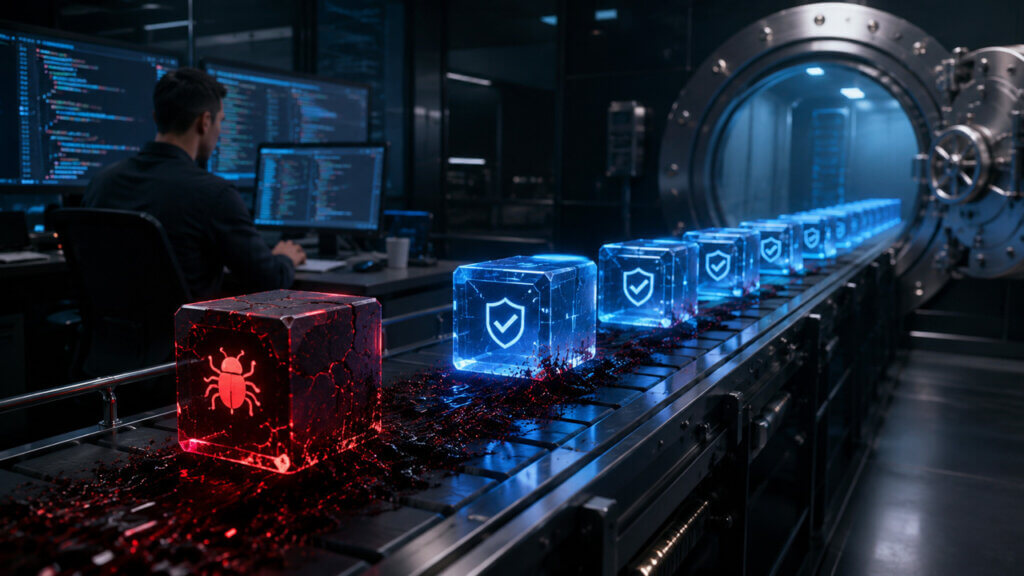
After onboarding, repository permissions and review become the core safeguards. UK National Cyber Security Center guidance recommends making repository activity attributable, reviewing every production-bound change, applying extra scrutiny to external contributions, and revoking access quickly when it is no longer required. Hardware-backed credentials can protect an account from credential theft, while tightly scoped permissions and independent review limit what an authorized account can change.
Related Reading
A new malware campaign targeting crypto developers shows how attackers can move upstream, stealing GitHub tokens, SSH keys, cloud credentials, wallets, and environment variables before a protocol ever ships vulnerable code.
May 26, 2026
·
Gino Matos
CryptoSlate reported on July 5 that operational compromises around keys, custody, signing and approval systems accounted for roughly 76% of stolen value during the first half of 2026, even though smart-contract exploits were more frequent. That gap shows why access and operational controls matter even when they account for fewer incidents.
Wallet and protocol teams should treat contractor access as continuously conditional. Identity checks should extend through employment, third-party firms should be audited, repository privileges should remain narrow and observable, every production-bound change should receive independent review, and access should be revoked as soon as it is no longer required.
Consensys’s April release pause also shows the value of retaining a predefined way to halt changes while suspicious access is investigated.
S&P’s Vault Risk Assessment weighs six risks in DeFi lending as vault deposits reach $10 billion, but it is not a credit…
S&P’s Vault Risk Assessment weighs six risks in DeFi lending as vault deposits reach $10 billion, but it is not a credit…
The stock trading platform seeks to offer tokenized shares in more than 60 US-listed companies under the SEC’s recently introduced innovation exemption.
Tokenized stocks market supply is at $3.2B and projected to hit $2T by 2028-2030.